Fined for not looking: three 2025 HIPAA penalties, one risk analysis requirement
Warby Parker, Health Fitness and Northeast Radiology had three different breaches, and the regulator cited the same HIPAA Security Rule requirement each time. This guide gives you a worked risk-analysis entry for each case, the AWS WAF controls that answer it, and a blank worksheet for your own systems.
$1.5M
Largest of the three penalties
3 years
About how long one exposure ran before it was found
1
Requirement cited in all three cases
Free PDF, 15 pages. Published October 2026 by safeINIT, an AWS Advanced Tier Services Partner.
Three 2025 HIPAA enforcement actions, one citation
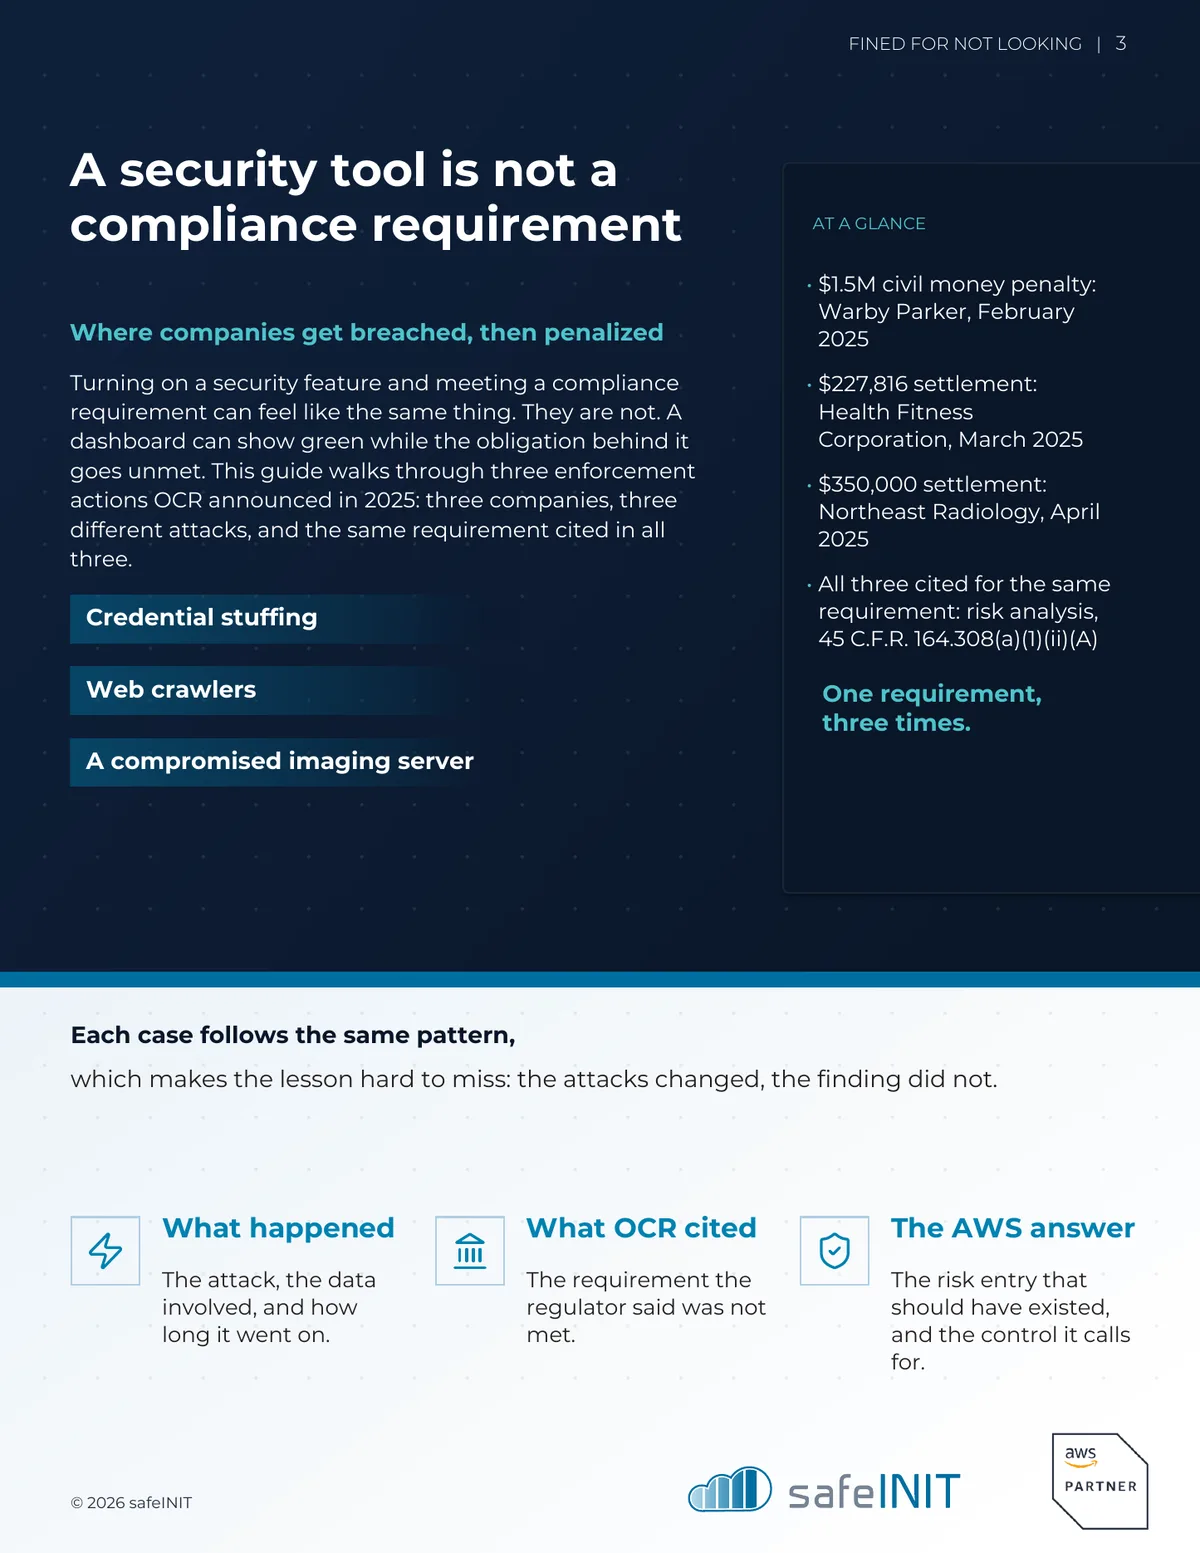
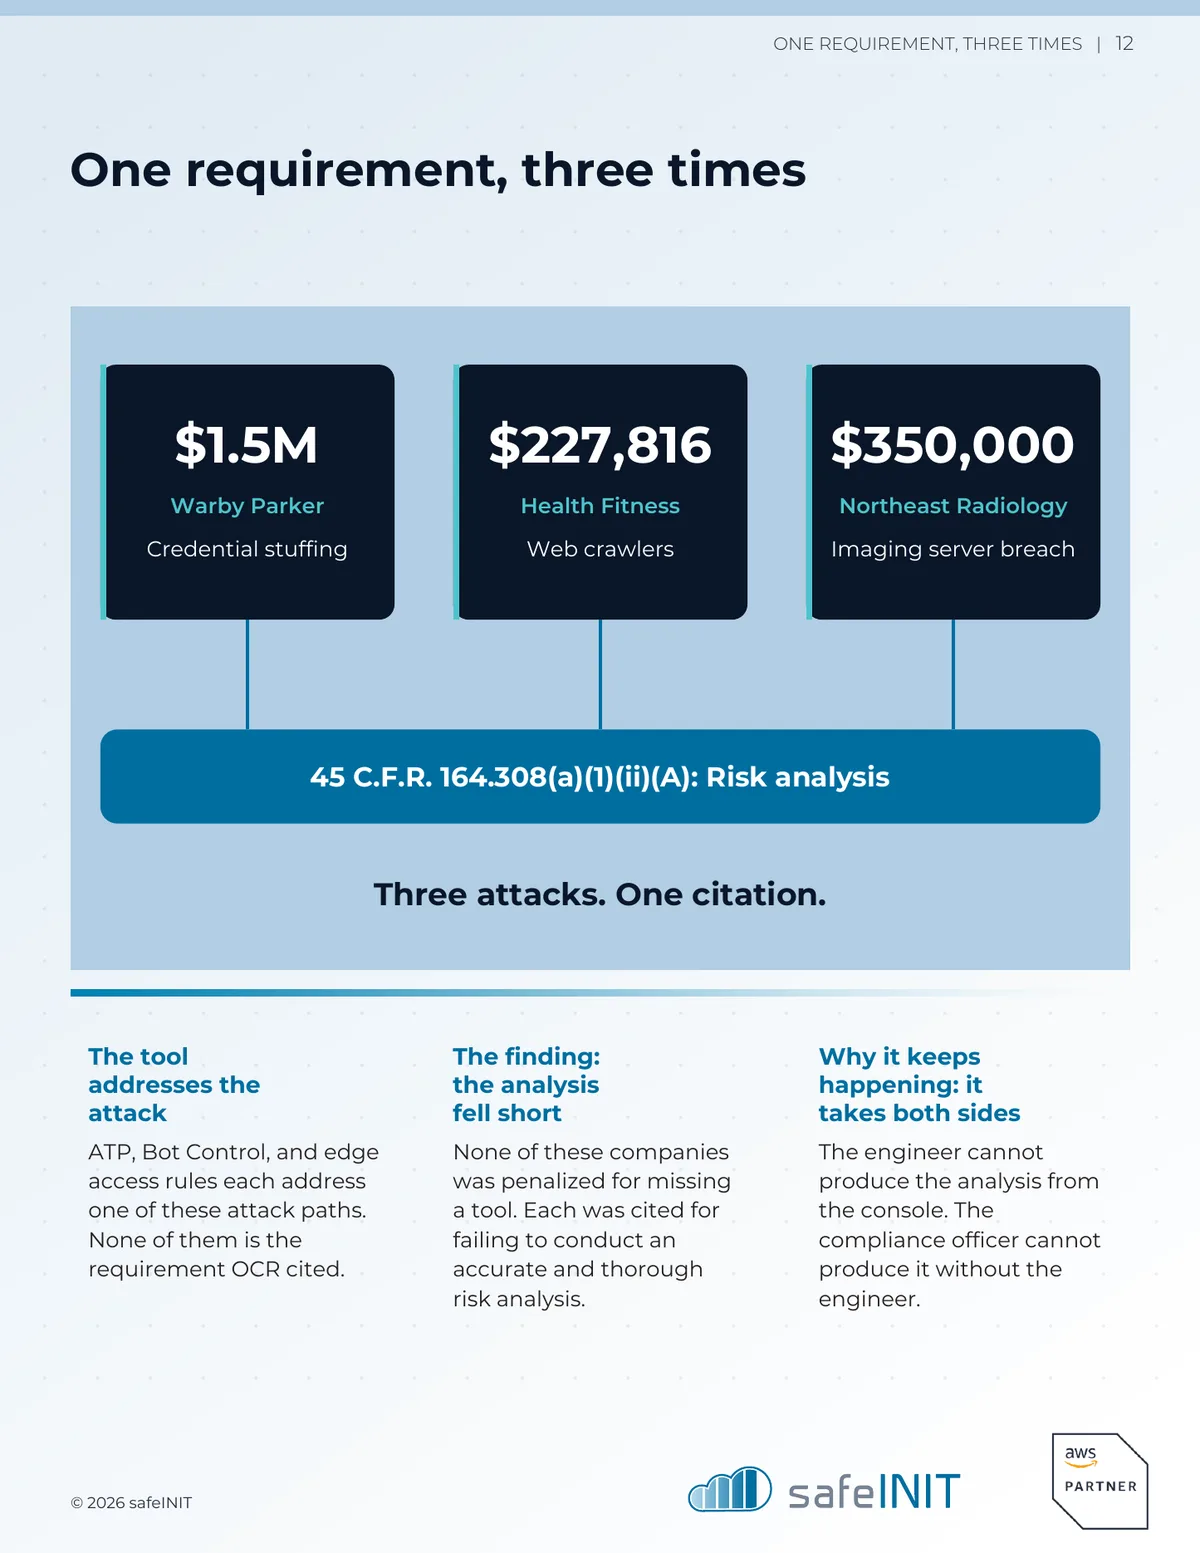
They weren't fined for being breached. They were fined for not looking. Three companies, three different attacks, and the HHS Office for Civil Rights cited the same HIPAA Security Rule requirement in all three: risk analysis.
Warby Parker
Credential stuffing
$1.5M
Civil money penalty, announced February 2025
Attackers replayed usernames and passwords stolen in unrelated breaches against customer accounts. 197,986 people were affected, and the data included eyewear prescriptions.
The AWS answer
AWS WAF Account Takeover Prevention on the login path.
Source: HHS Office for Civil RightsHealth Fitness Corporation
Web crawlers
$227,816
Settlement, announced March 2025
A software misconfiguration left ePHI on a server discoverable on the internet and exposed to automated crawlers from 2015 until it was found in 2018. No attacker was needed.
The AWS answer
Access control first, then AWS WAF Bot Control at the edge.
Source: HHS Office for Civil RightsNortheast Radiology
Imaging server breach
$350,000
Settlement, announced April 2025
Unauthorized individuals accessed radiology images on a PACS server between April 2019 and January 2020. The practice notified 298,532 patients.
The AWS answer
AWS WAF IP sets, geo rules and rate-based rules at the edge, with network rules for non-HTTP imaging traffic.
Source: HHS Office for Civil Rights
45 C.F.R. 164.308(a)(1)(ii)(A)Risk analysis
Three attacks. One citation. Read the requirement in the eCFR
Written from a live session with AWS
Cosmin Drimba, CEO and co-founder of safeINIT, presented the three cases in September 2026. Radu Dobrinescu, Senior Partner Solutions Architect at AWS, walked through the AWS WAF configuration for each one in the console. The recording is below, and the slides are on the event page.
What's inside: worked risk-analysis entries and the AWS WAF configuration
A green dashboard is not proof of compliance. The compliance officer owns the HIPAA obligation, the auditor owns the evidence, and the engineer owns the AWS console. Each does their job correctly, and the breach happens between them. The guide is written for all three to read.
The cases, with sources
What happened, what the regulator cited, what it cost
Each case follows the same pattern: the attack, the data involved and how long it went on, then the requirement the regulator said was not met. Sources are listed with each case.
The paperwork
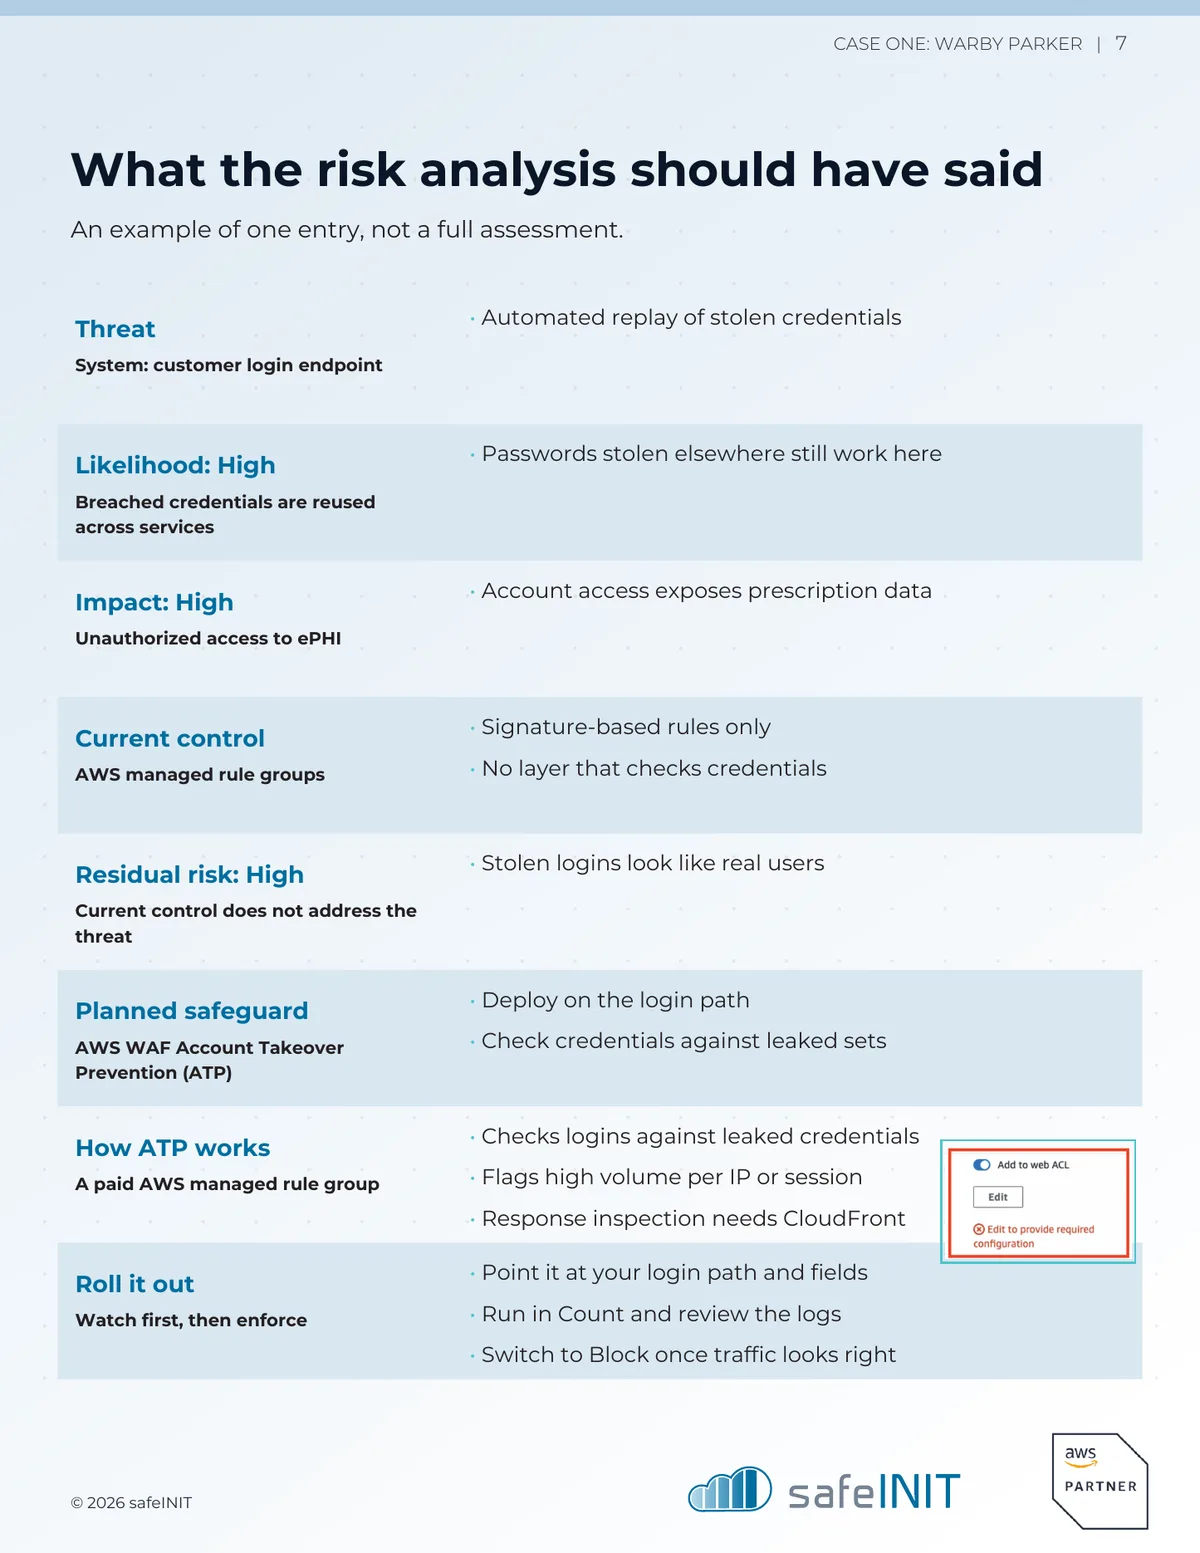
What the risk analysis should have said
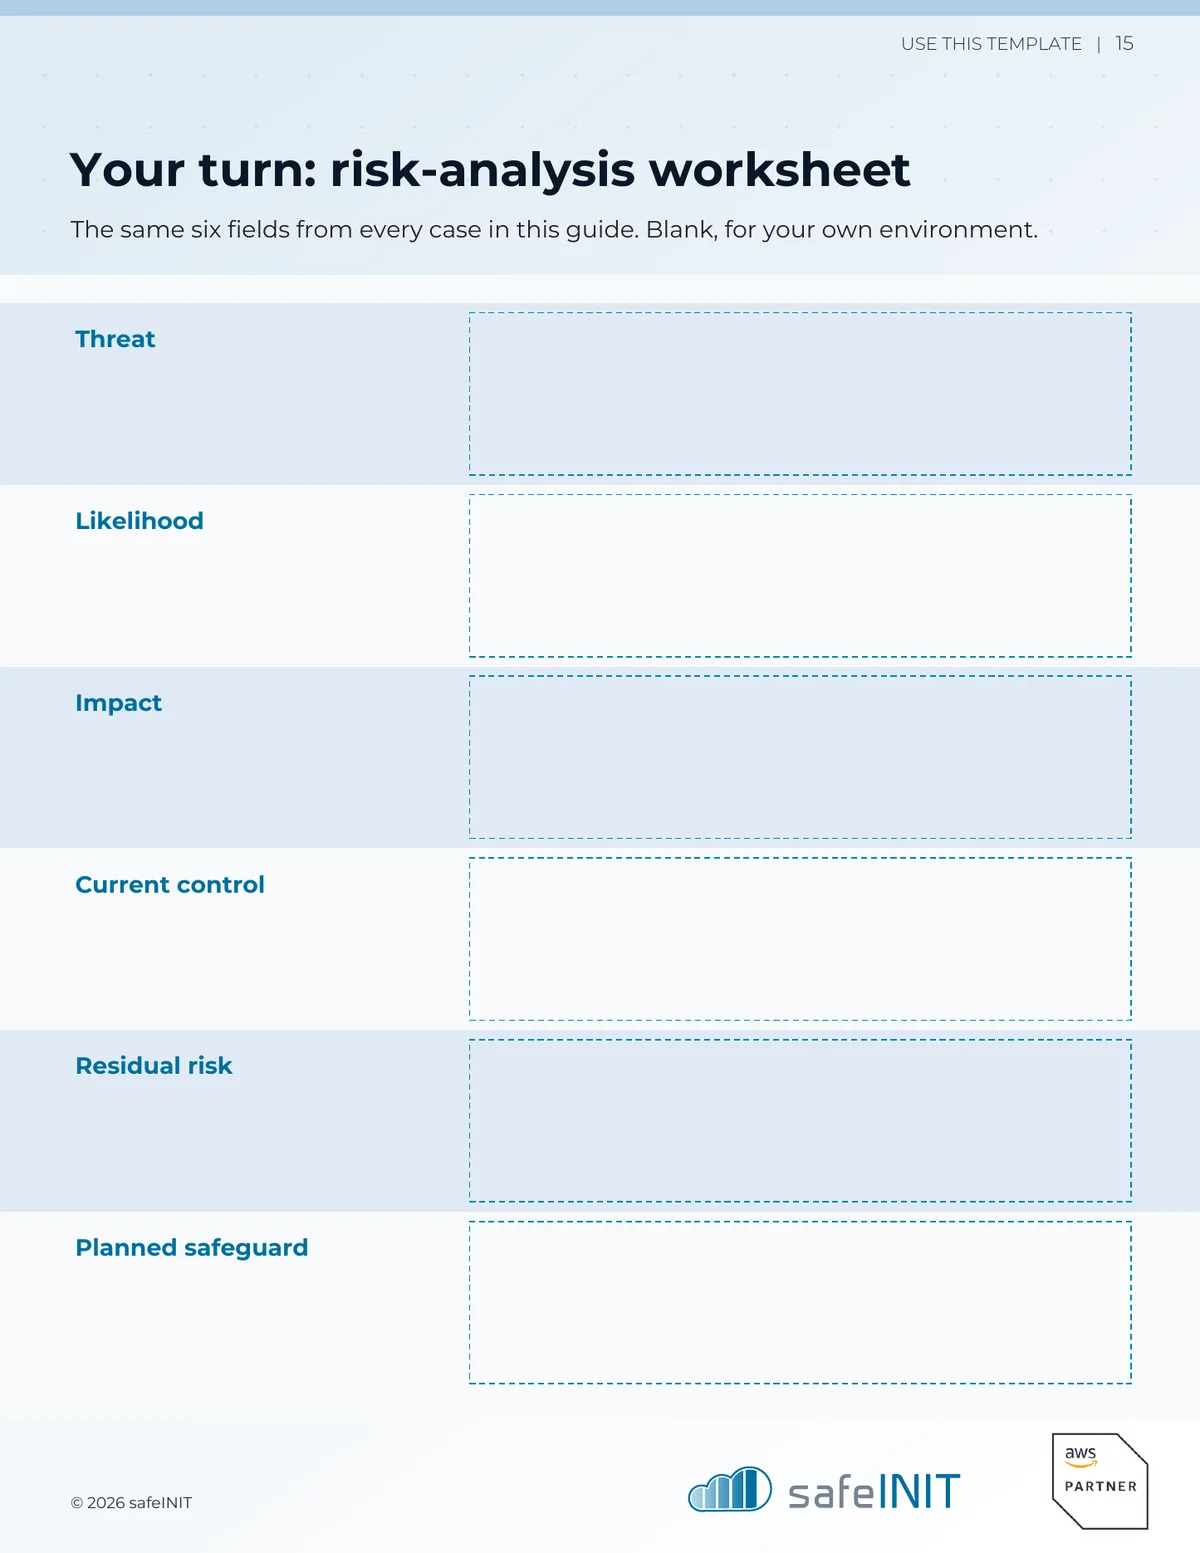
For each case, a worked example of one risk-analysis entry: threat, likelihood, impact, current control, residual risk and planned safeguard. An example of one entry, not a full assessment.
The console
The AWS WAF configuration behind each safeguard
Account Takeover Prevention, Bot Control and edge access rules: how each one works, what it does not cover, and how to roll it out in Count mode before you switch to Block.
Your turn
A blank worksheet for your own environment
The same six fields from every case, empty. Fill in one entry per system that holds ePHI and you have the start of the analysis an auditor asks for.
Frequently asked questions
Common questions about the guide and how we handle your details.
Want to know where you stand?
The free assessment scores your AWS setup and sends the results to you by email. Look before someone else does.